01 · unsafe pasteRaw stays local
“Draft the appeal for patient Delia Marchetti, MRN 4471902, plan ID BCX99188342.”
Customer-hosted Sector policy Chain verified
One customer-owned control point between sensitive work and an approved model. Policy runs first; operating evidence stays with you.
The sample pack
This is a real Evidence Pack generated by Ledgerproof for a fictional six-person firm over the 2026 filing season. Synthetic data, real product, nothing gated.
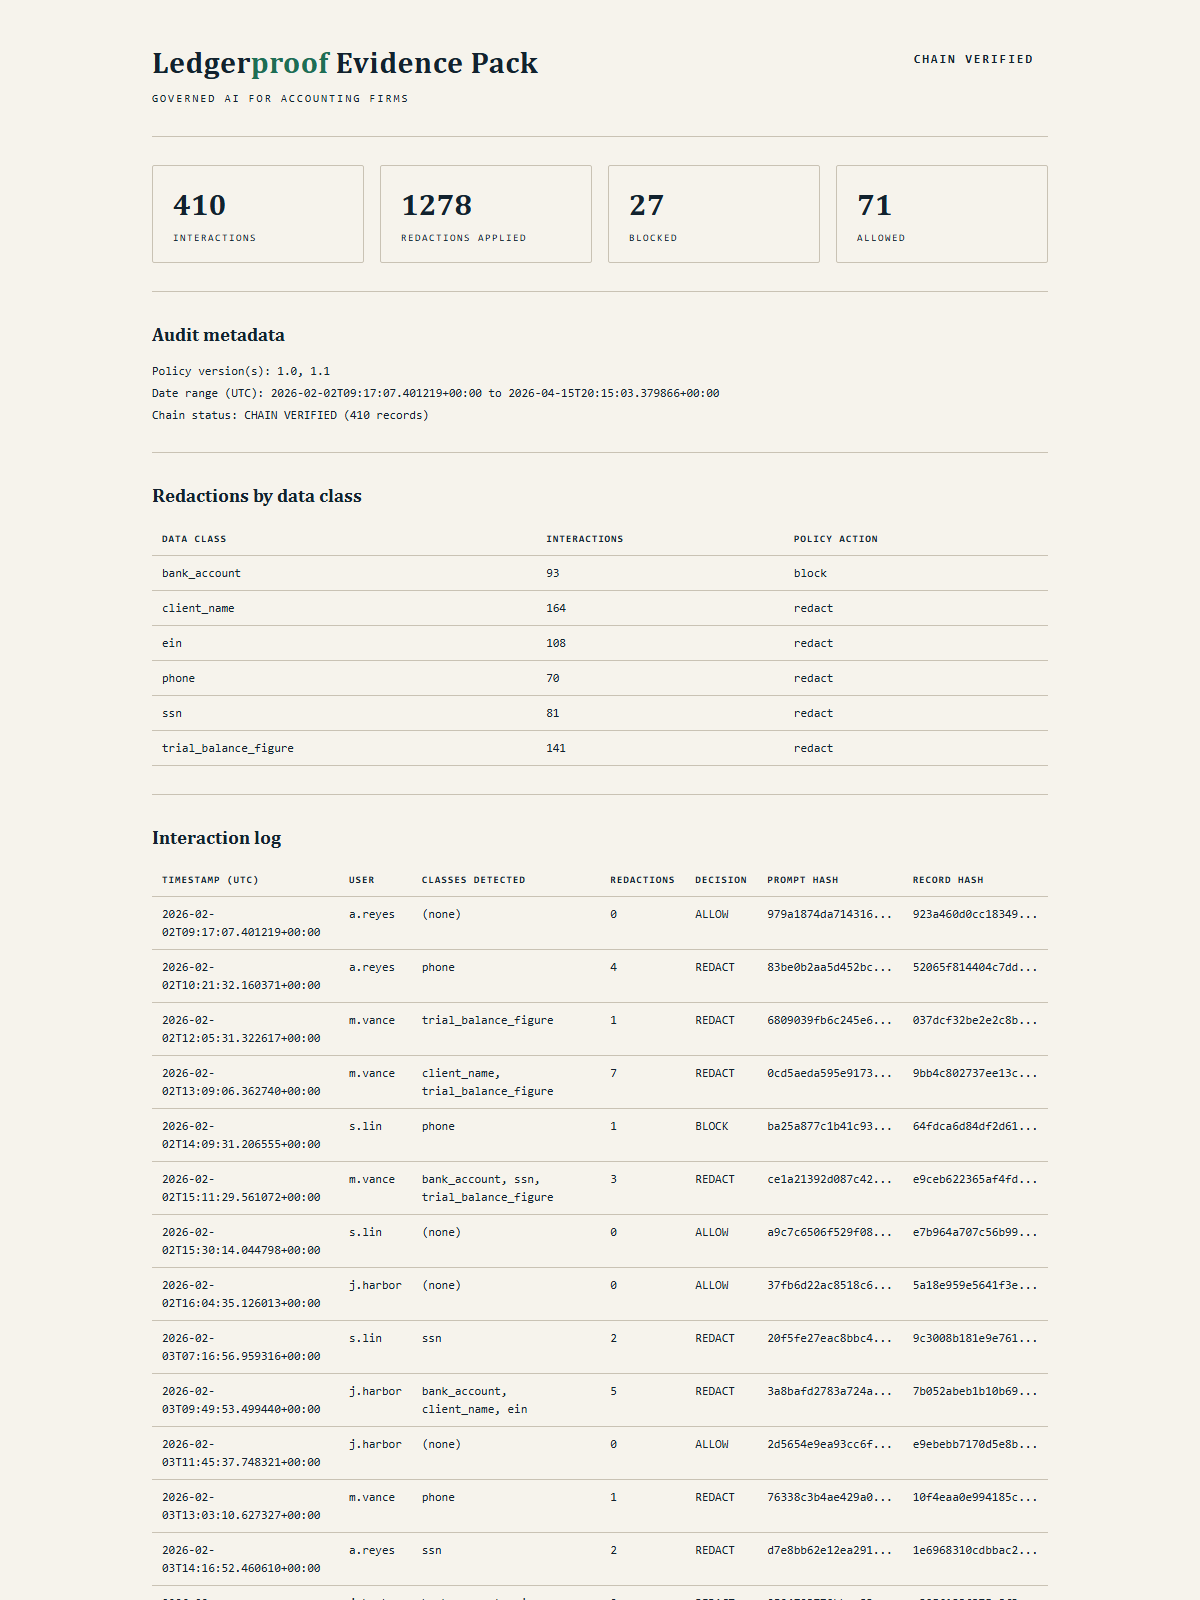 Harbor and Vance CPAsSample Evidence Pack · synthetic data
What is in the file
Firm, period, policy versions, chain status.
Record count, first and last hash, verification result.
Interactions by user and backend, week by week.
Counts for SSN, EIN, account, client name, and trial balance figures.
Every block event with the policy version and staff user.
A documented review of AI output.
Honest scope: the pack attests to what flowed through the gateway. It does not claim to see what never touched it.
The live control
Try a synthetic sector example or write your own. This illustrative pass runs only in your browser; nothing is sent anywhere.
LedgerProof Health
Start with one administrative text workflow—follow-up instructions, prior-authorization language, or an internal policy draft. Direct identifiers can block the request; lower-risk classes can become typed tokens before an approved model sees the prompt.
Policy-controlled masking is not, by itself, a HIPAA de-identification determination or compliance certification. The customer’s privacy, security, and legal owners remain in charge.
“Draft the appeal for patient Delia Marchetti, MRN 4471902, plan ID BCX99188342.”
MRN and plan ID are forbidden classes. Nothing reaches the model; the event is still recorded.
“Draft the appeal for PATIENT_NAME_1. Keep the rationale administrative and route it for clinician review.”
Every unapproved prompt can carry a Social Security number, an EIN, or a client ledger. Right now, most firms have no durable record of what left, when, or to whom.
What gets installed
Detection, policy, redaction, backend choice, and the evidence chain. One owned system in your environment.
Swipe to inspect the installed stack →One internal endpoint staff use instead of raw chatbots. Every request passes through the same rules.
FastAPI · local or private cloudAllow, redact, or block per data class in a YAML file a control owner can read.
Fail-closed defaultsThe same control inside Claude Desktop through a governed tool with the chain already baked in.
Installed in minutes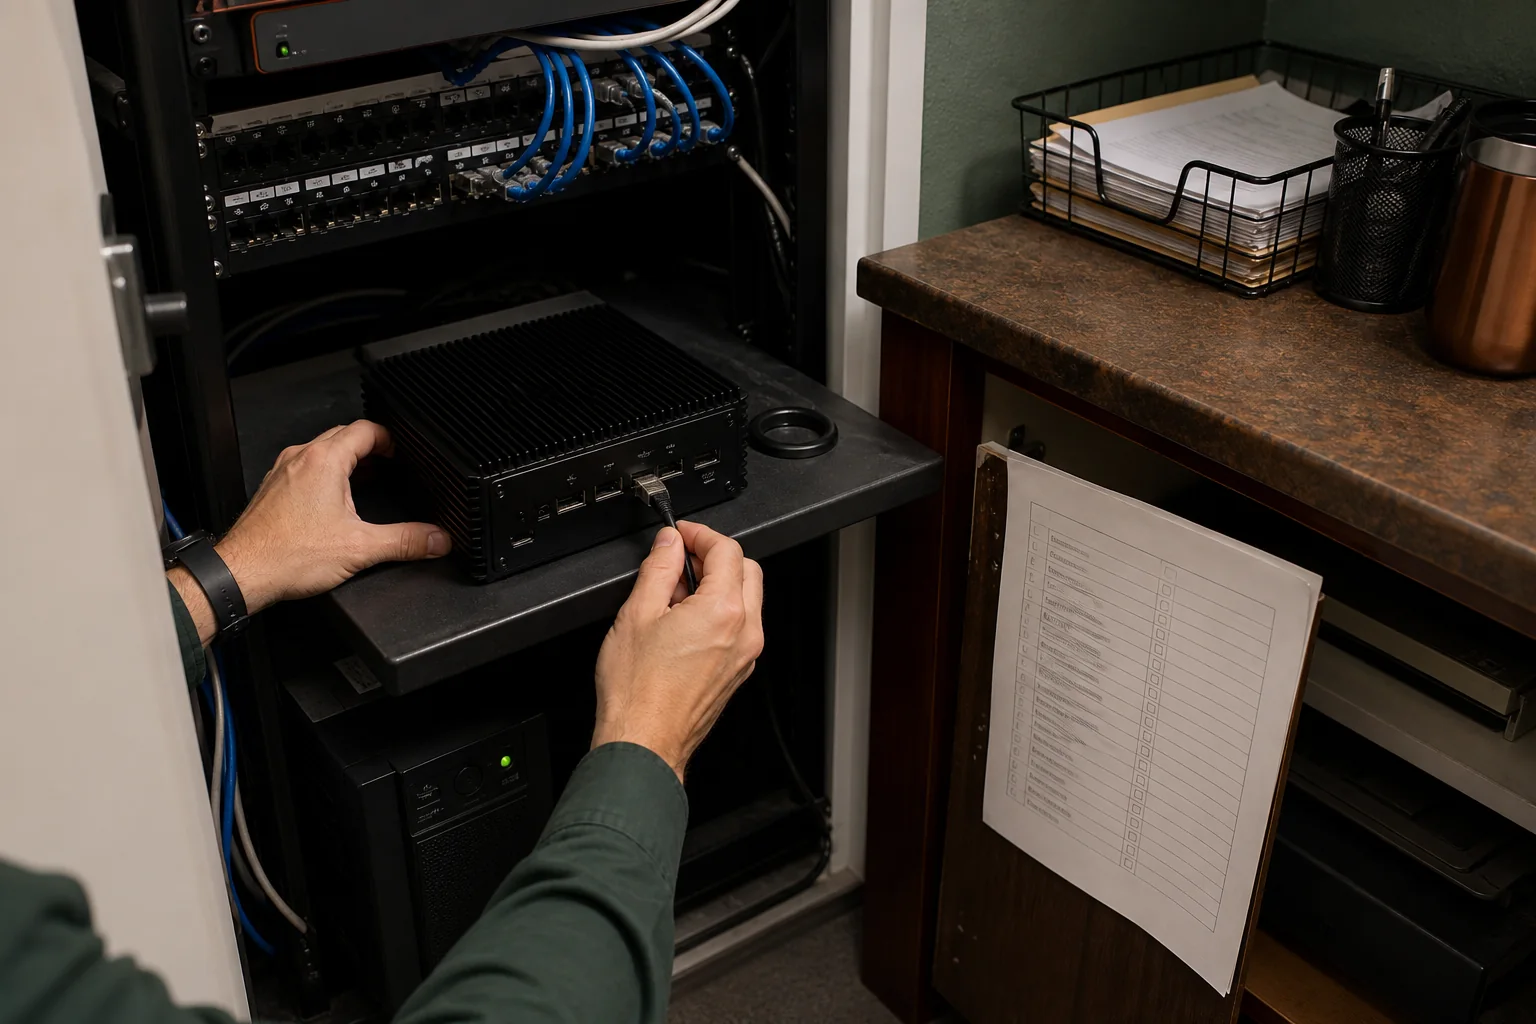
Your box, your keys, your policy, your log.
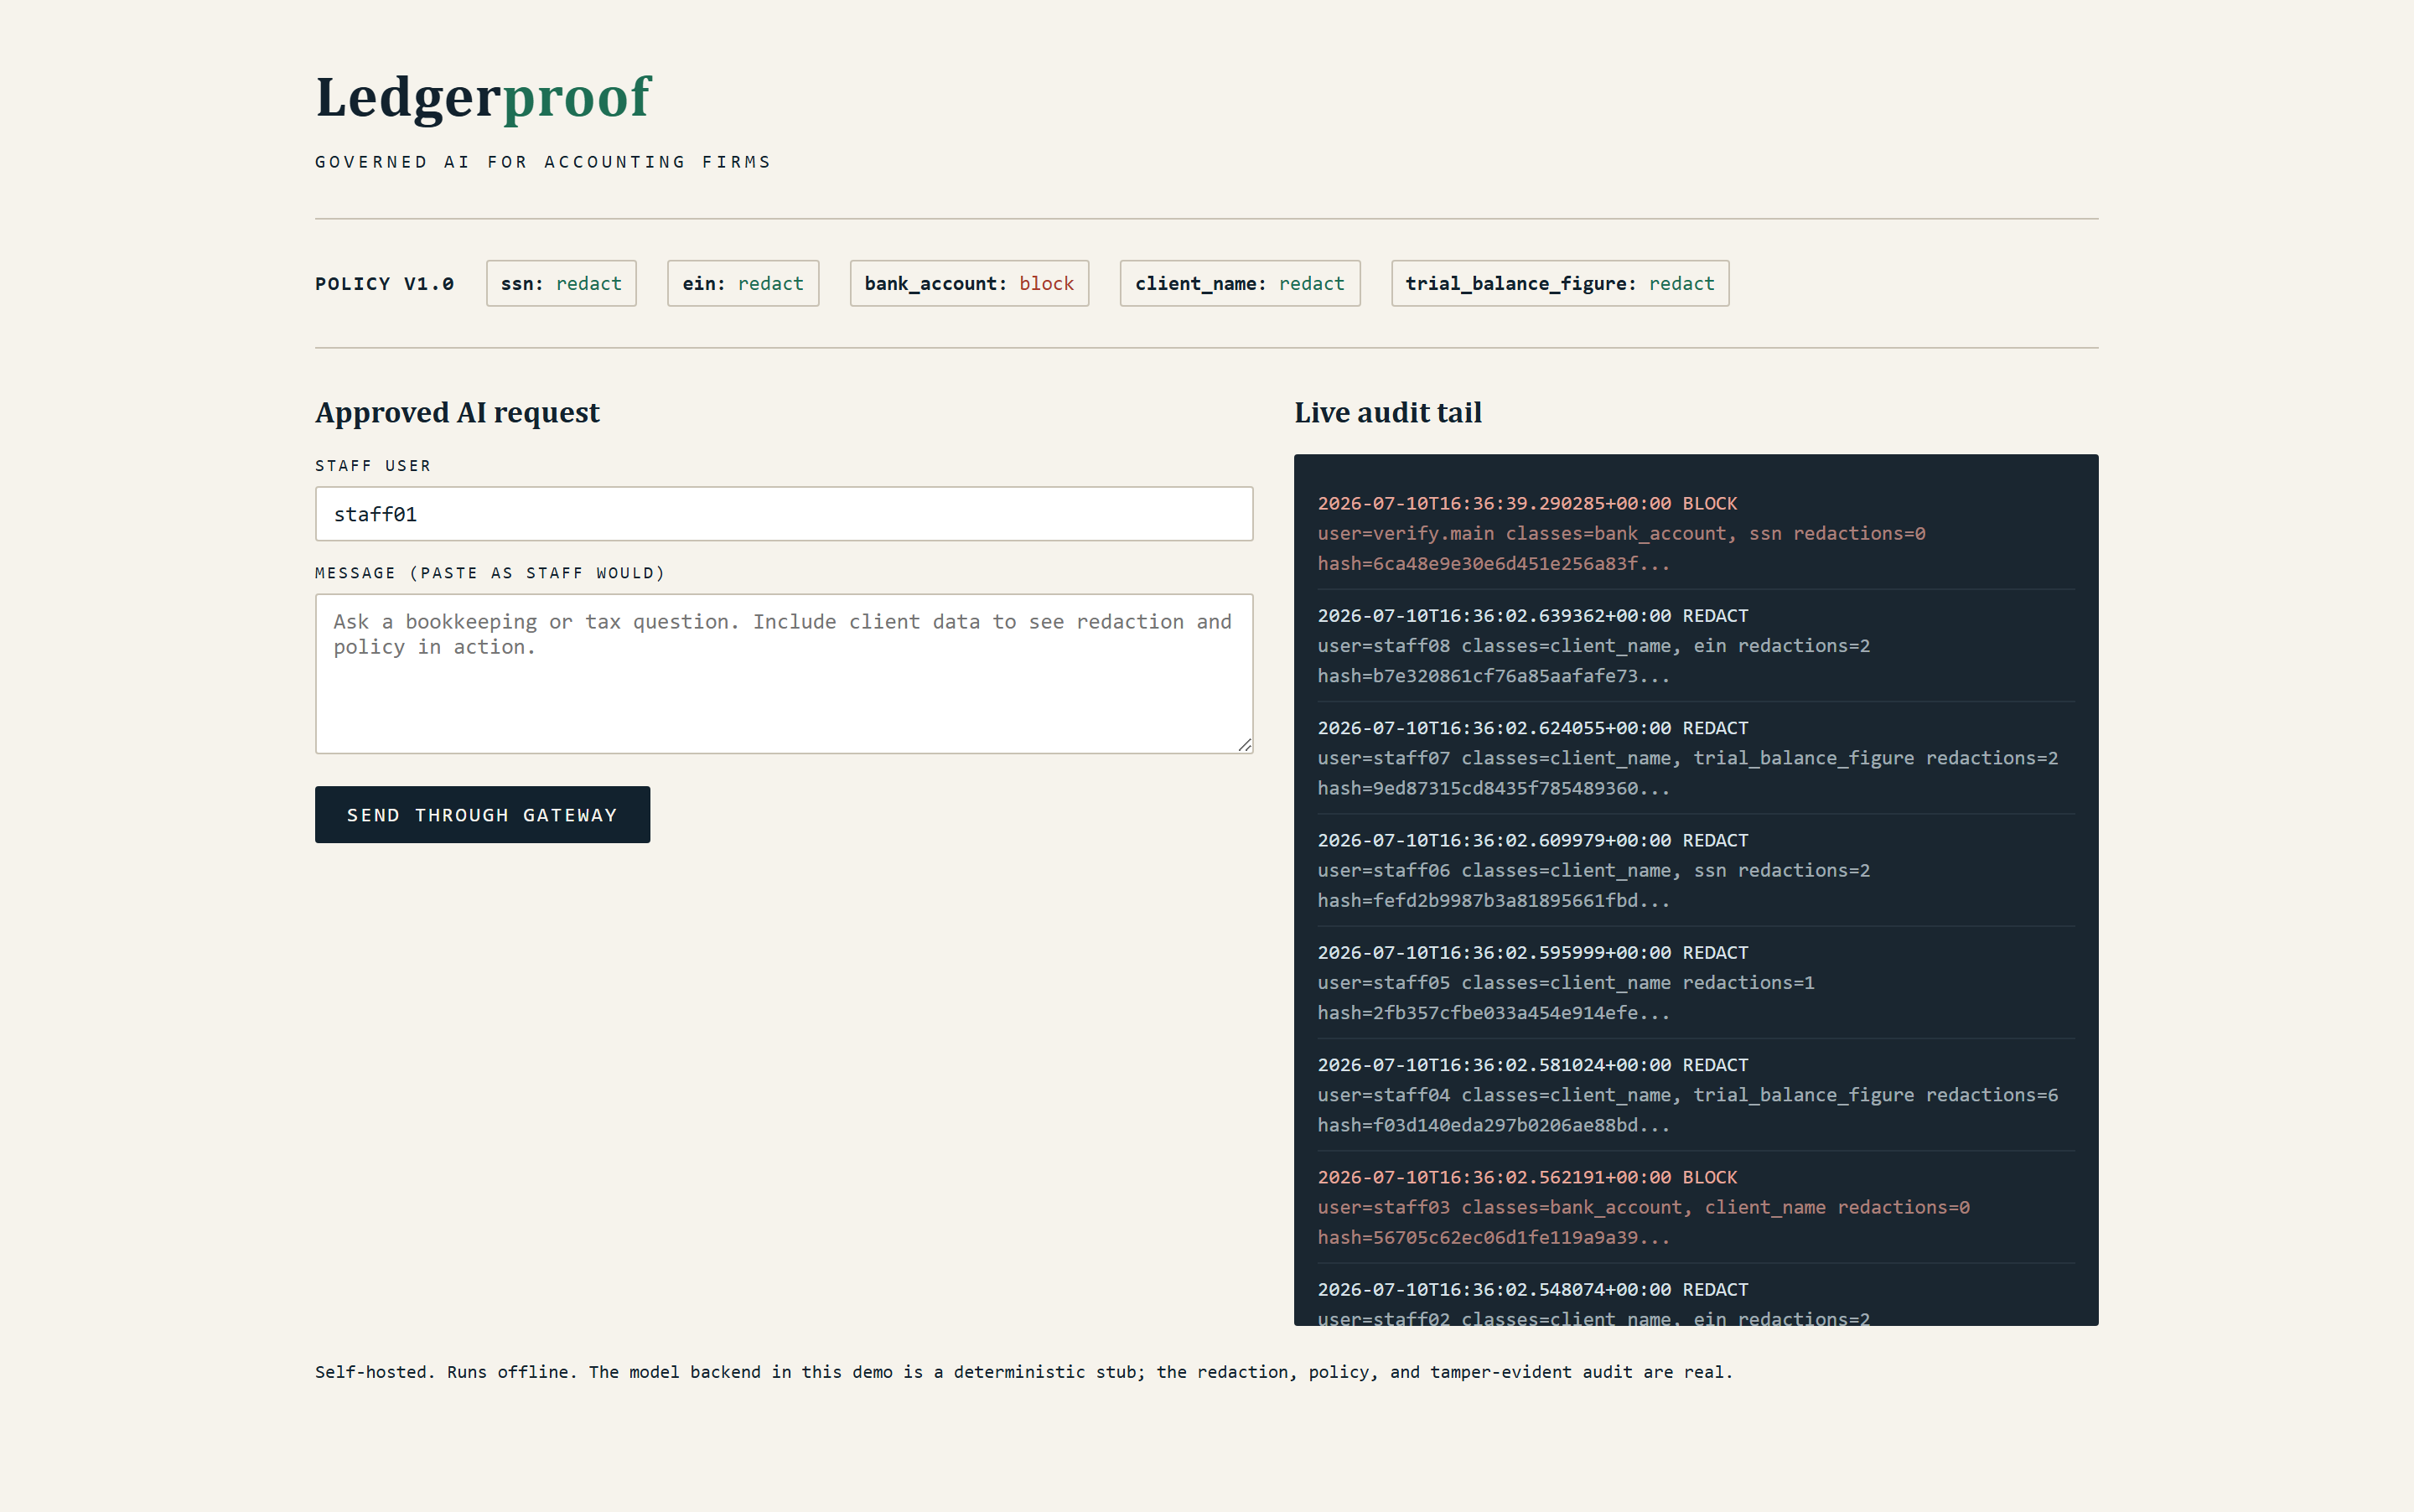
The actual operator surface, not a design mockup.
The engineered peak
Each record carries the hash of the record before it. Alter one event and every proof downstream breaks.
Swipe the records → record 03 is editable.
5fecd5c9320c4e4f81148dde28d69e2f$ ledgerproof verify audit.jsonl
CHAIN VERIFIED (5 RECORDS)
Sealed. Every hash matches the record and its predecessor.
The evidence map
Read across: the pack section, the control it demonstrates, and the question it helps answer. Your counsel confirms the mapping for your firm.
Which rules were in force for each interaction.
Who used which approved backend and when.
Which client-data classes were removed before forwarding.
Every exception with user, decision, and policy version.
Whether the operating record has been altered.
Who reviewed the output, and when.
Sources: 16 CFR Part 314; IRS Publication 4557; IRS OPR guidance 2026-19. This is an engineering mapping, not legal advice.
The second sentence is where paper-only programs fail. Ledgerproof supplies the operating record, while keeping the boundary honest.
Owned outcomes
You buy a working control and its evidence, not seats on a meter that reprices every year.
Swipe to compare the three starting points →Map before you move
Exposure map, sector-aware policy draft, synthetic acceptance tests, and a first Proof Folder.
Find my starting pointControlled teams
One approved workflow live, staff onboarded, tested policy, operating runbook, and the first verified Evidence Pack.
Plan the installStay current
Monthly chain check, quarterly pack, exception summary, guidance bulletin, and owner review.
Check assurance fitMore than one office or identity domain?
Scoped by environments, identity, integrations, and policy tiers—never by seat. Wider rollout begins only after the pilot proves the operating and evidence model.
Scope the pilot →A guided starting point
Ledgerproof is not only an SSN masker. The policy changes with the data, workflow, and control environment—from tax identifiers and payment rails to health-plan IDs, medical record numbers, network details, and confidential control evidence.
What you receive in 15 days
Built and installed by one accountable person
Umair Tareen brings twelve years in enterprise data, including a decade across banks and six years at MUFG. Those systems lived under audit. Ledgerproof's habits come from that environment: redaction pipelines, append-only logs, and evidence that survives hostile review.
He installs Ledgerproof personally, in your environment, and you keep what he builds.
No. There are no LedgerProof servers in the data path. The gateway runs on customer-controlled infrastructure, and model keys stay there.
OpenAI, Anthropic, or fully local through Ollama. Your keys, your choice, configurable per install. The public demo uses a deterministic local stub.
Nothing technical, and anyone claiming otherwise is selling surveillance. The install pairs a governed path with a signed policy and staff onboarding. The Evidence Pack states exactly what the control covers.
Those are real controls and may be the better fit for their native environments. Ledgerproof is compelling when you want a smaller self-hosted, model-neutral boundary with a readable policy, local metadata-only audit trail, and portable evidence you can verify offline. It complements an enterprise security stack rather than pretending to replace one.
Yes. The shipped profiles cover accounting and payment data plus text-based healthcare and bank-risk identifiers such as EINs, accounts, names, dates, MRNs, NPIs, plan IDs, addresses, email, phone, IPs, device IDs, licences, vehicles, and biometric references. Detection is contextual and must be tested against each customer's synthetic examples before live use.
No. The install is scoped by environment, workflow, backend, and support boundary. The customer owns the gateway, policy, log, and every Evidence Pack. Quarterly assurance is optional.
No. Ledgerproof is an engineering control mapped to professional duties. Your counsel and your judgment stay in charge.
A 15-minute walkthrough
Tell Umair the team size, sector, and first workflow. You will get two time options within two business days.